5 AI cybersecurity opportunities hiding in ordinary workflows
Many security failures begin inside routine email, access, vendor and support processes long before an alert reaches the security operations center.
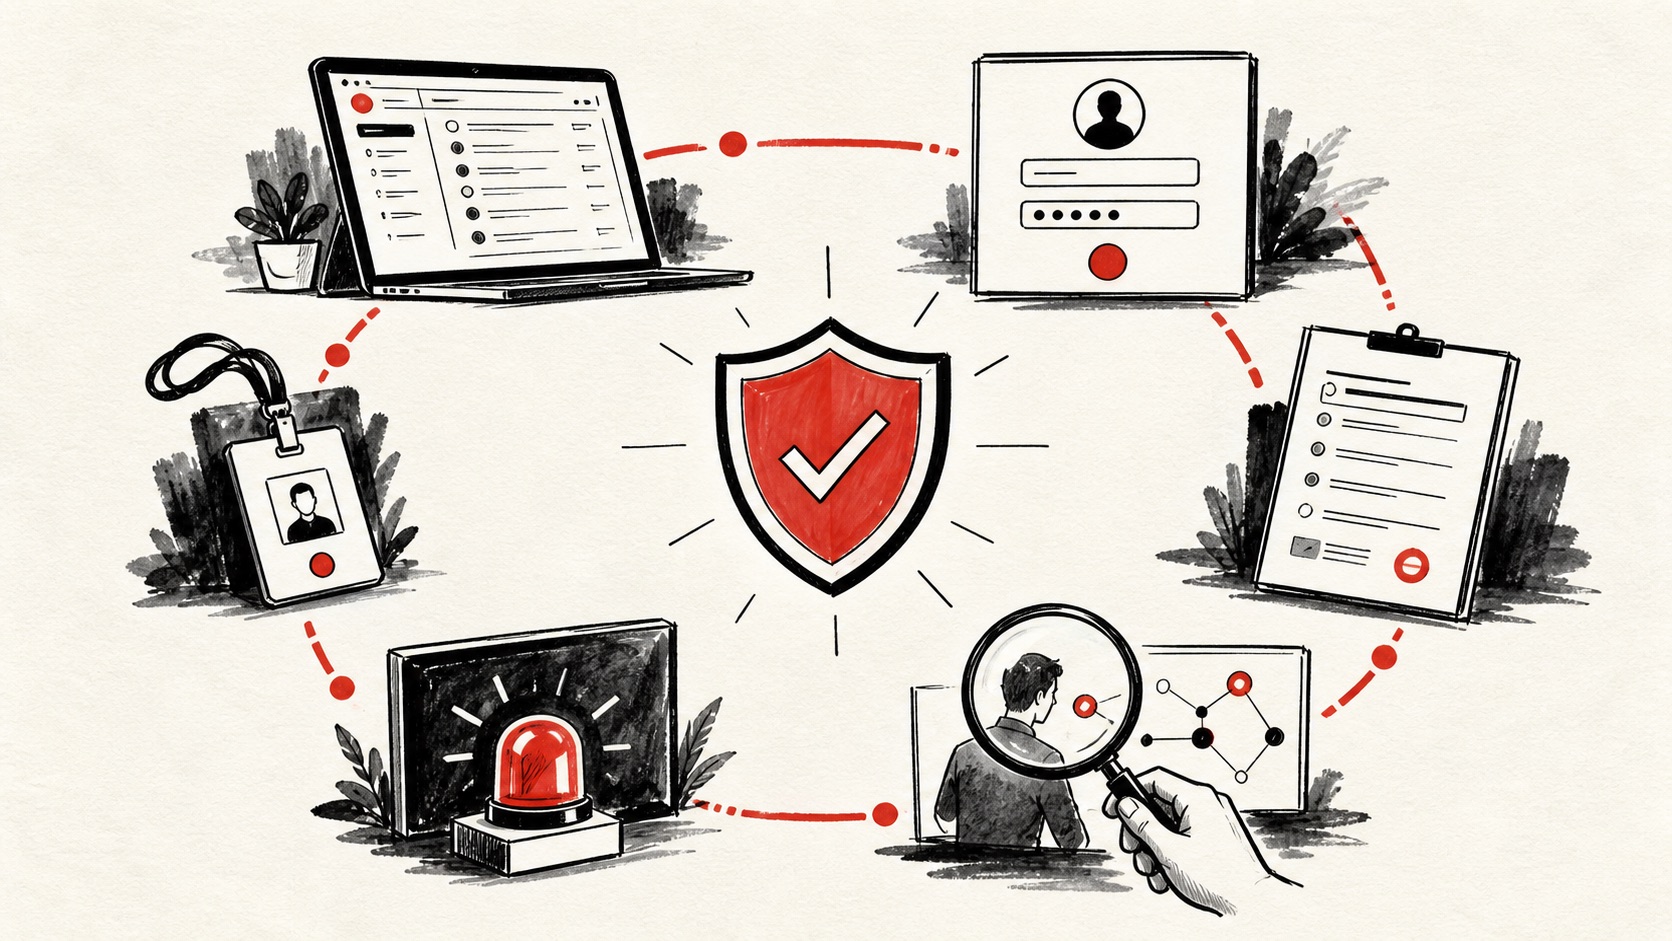
Security teams have no shortage of alerts. The better opportunity is to improve the everyday workflows that create identity, move sensitive data and grant trust to outside parties.
These services can begin with bounded review tasks and visible evidence. They support analysts without giving a model authority to make irreversible security decisions.
Three tests for a useful opportunity
The system is strong enough for the job without paying for unnecessary capacity.
Security, latency and maintenance are practical for the intended operator.
The advantage grows through data, workflow depth, distribution or trust.
This ranking is an editorial framework, not a forecast or promise of financial results.
The ranking at a glance
Five practical pathsVendor security response analysis
Extract claims, control evidence and unanswered questions from questionnaires and assessment documents. Reviewers can compare vendors consistently while retaining the final risk decision.
Marketing statements should never be treated as verified controls.
Access review preparation
Group permissions by role, highlight unusual combinations and assemble manager review packets. The product reduces preparation time while accountable owners still approve or remove access.
Historical usage is context, not automatic justification for access.
Phishing report enrichment
Combine message headers, sender history, link analysis and similar reports into a concise analyst brief. Employees receive a faster response and analysts avoid repeated collection work.
Automated analysis should occur in an isolated environment.
Sensitive data movement review
Explain why a file transfer, email attachment or shared link may violate policy using surrounding business context. Reviewers can distinguish legitimate work from risky behavior more efficiently.
Employee monitoring requires transparent policy and careful access.
Security ticket normalization
Turn inconsistent reports into structured incident fields, identify missing facts and route the ticket to the correct queue. The system improves intake without declaring severity on its own.
Critical keywords and emergency routes should use deterministic rules.
Reduce ambiguity before adding autonomy
Security products gain trust when they assemble evidence, enforce a consistent intake and make the analyst’s decision easier. Autonomous enforcement should follow only after rigorous evaluation.
Get the free 25 AI Offers field guide.
Practical starting points, buyer problems and offer angles for the AI economy. Download it now and get the next useful briefing.